-20%

Cloud Intrusion Detection using Optimized Neural Networks

0 Orders 0 Wish listed

₹4,999.00

Qty
Total price:
  ₹4,999.00

Detail Description

1. Abstract

Cloud Intrusion Detection using Optimized Neural Networks is a cybersecurity project designed to identify malicious activities and unauthorized access attempts in cloud computing environments. The system analyzes network traffic and cloud security data using neural networks optimized through techniques such as hyperparameter tuning, feature selection, and learning-rate optimization. The trained model classifies network activities as normal or potentially intrusive, helping identify threats such as denial-of-service attacks, unauthorized access, and suspicious network behavior. An interactive dashboard presents intrusion predictions, security alerts, and model performance metrics. The project aims to improve cloud security monitoring by combining neural-network-based threat detection with efficient model optimization.

2. Objectives

  1. Develop a neural-network-based intrusion detection system for cloud environments.
  2. Analyze network traffic and security-related features to identify suspicious activity.
  3. Optimize neural-network parameters to improve detection performance.
  4. Classify network records as normal or potentially malicious.
  5. Detect supported intrusion categories using labeled datasets.
  6. Evaluate model performance using precision, recall, F1-score, and false-positive rate.
  7. Develop a dashboard for intrusion monitoring and visualization.
  8. Reduce manual effort in identifying potential cloud security threats.

3. Existing System

Traditional cloud intrusion detection systems often rely on predefined rules, signature-based detection, and conventional machine-learning algorithms. These approaches can identify known attack patterns but may struggle with complex traffic relationships, changing attack behavior, and large volumes of cloud network data.

Disadvantages

  1. Signature-based methods may miss previously unseen attacks.
  2. Fixed detection rules may not adapt well to changing traffic patterns.
  3. Large datasets can increase training and processing requirements.
  4. Poorly tuned neural networks may produce inaccurate predictions.
  5. False positives can generate unnecessary security alerts.
  6. Some systems provide limited visualization of model performance and detected threats.

4. Proposed System

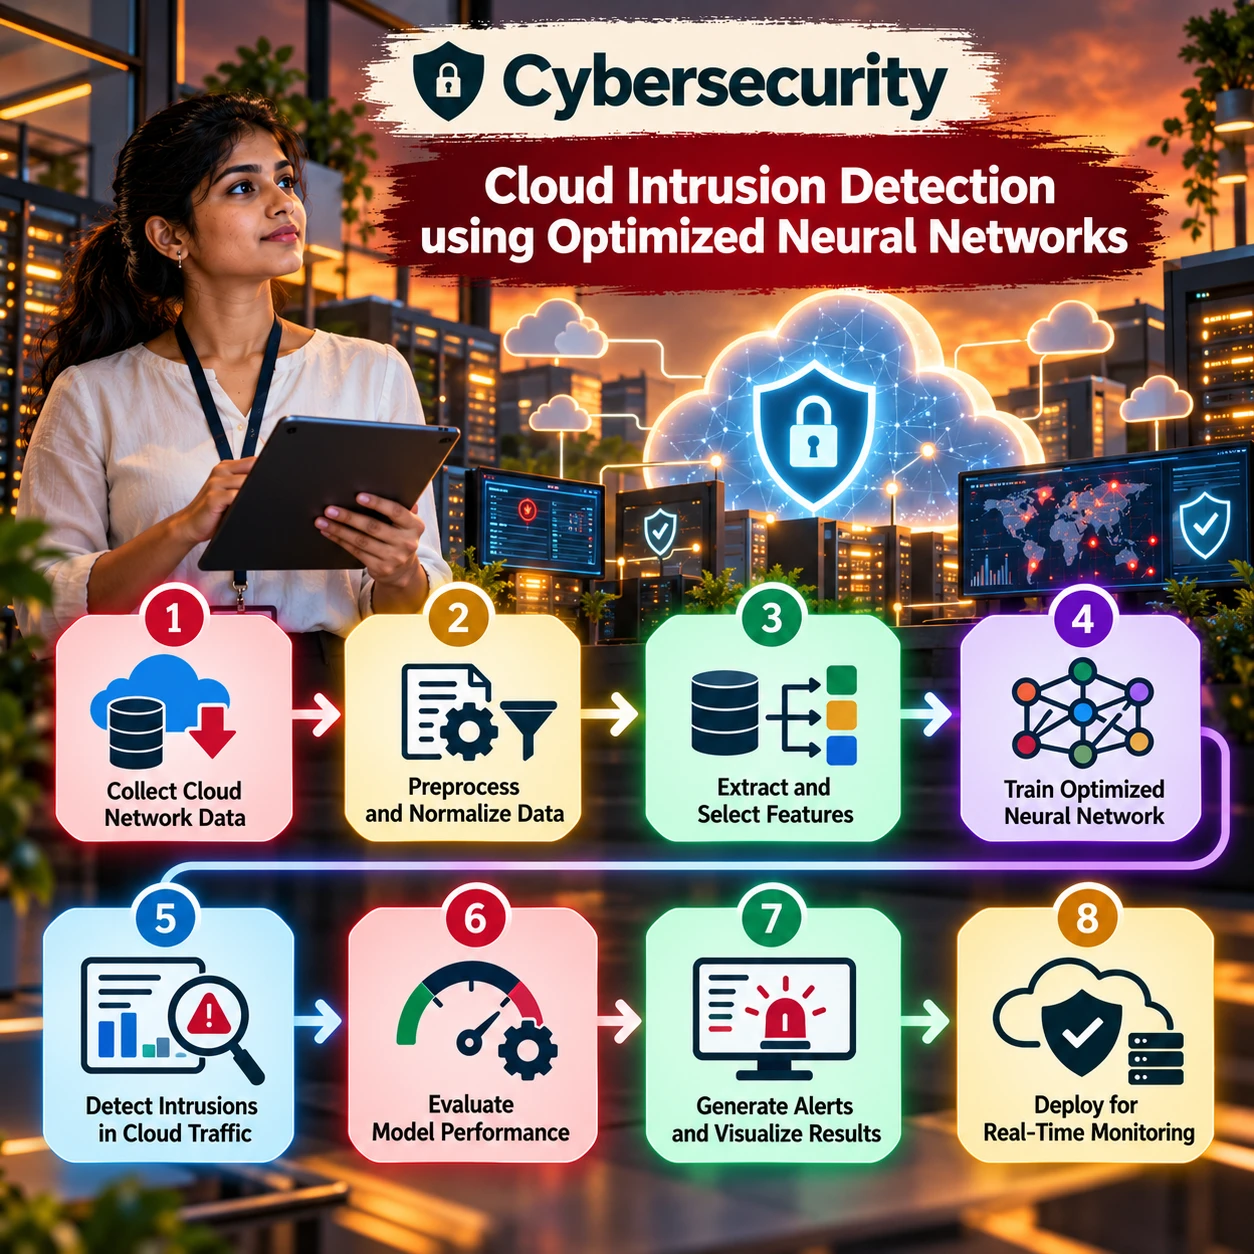
The proposed system uses an optimized neural network to detect potentially malicious activity from cloud-related network traffic or intrusion detection datasets. It preprocesses the input data, selects relevant features, trains a neural-network classifier, and optimizes model parameters using validation data. The trained model predicts whether network activity is normal or intrusive and displays results through a security dashboard.

Key Features

  1. Cloud Traffic Analysis: Processes network-flow and security-related features.
  2. Data Preprocessing: Handles missing values, categorical attributes, normalization, and class imbalance.
  3. Feature Selection: Identifies relevant features to reduce unnecessary model complexity.
  4. Neural Network Classification: Uses an ANN or deep neural network for intrusion detection.
  5. Model Optimization: Applies hyperparameter tuning, regularization, and learning-rate optimization.
  6. Multi-Class Detection: Supports different intrusion categories when appropriate labels are available.
  7. Intrusion Alerts: Highlights suspicious records for investigation.
  8. Performance Dashboard: Displays accuracy, precision, recall, F1-score, and confusion matrix.
  9. Model Comparison: Compares optimized and baseline models.
  10. Deployment Extension: Supports integration with authorized cloud monitoring or traffic pipelines.

5. Implementation Procedure

  1. Requirement Analysis: Define the cloud environment, threat categories, and detection objectives.
  2. Dataset Collection: Obtain a suitable labeled intrusion detection dataset, such as CICIDS2017, CSE-CIC-IDS2018, or another relevant dataset.
  3. Data Preprocessing: Remove duplicate records, handle missing values, encode categorical features, and normalize numerical data.
  4. Exploratory Data Analysis: Examine class distributions, feature relationships, and attack patterns.
  5. Feature Selection: Use methods such as mutual information, correlation analysis, or feature importance to identify relevant attributes.
  6. Baseline Model Development: Train an initial neural network and record its performance.
  7. Model Optimization: Tune the number of layers, neurons, learning rate, batch size, regularization, and other hyperparameters using validation data.
  8. Model Training: Train the optimized neural network on the prepared dataset.
  9. Performance Evaluation: Calculate precision, recall, F1-score, confusion matrix, and false-positive rate. Use leakage-resistant data splits.
  10. Prediction Module: Classify unseen network records and generate intrusion alerts.
  11. Dashboard Development: Build an interactive interface using Streamlit or a web frontend.
  12. Testing and Deployment: Test on unseen data and, if required, integrate the model with an authorized cloud monitoring pipeline.

6. Software Requirements

  1. Programming Language: Python
  2. Deep Learning: TensorFlow/Keras or PyTorch
  3. Machine Learning: Scikit-learn
  4. Data Processing: Pandas, NumPy
  5. Visualization: Matplotlib, Seaborn, or Plotly
  6. Dataset: CICIDS2017, CSE-CIC-IDS2018, or a suitable cloud/network intrusion dataset
  7. Optimization: KerasTuner, Optuna, or Scikit-learn search utilities
  8. Backend: Flask or FastAPI, if required
  9. Frontend: Streamlit or React.js
  10. Development Environment: VS Code, Jupyter Notebook, or Google Colab
  11. Operating System: Windows or Linux
  12. Cloud Integration: AWS, Azure, or another platform if live monitoring is included

7. Hardware Requirements

Minimum Configuration

  1. Processor: Intel Core i5 or equivalent
  2. RAM: 8 GB
  3. Storage: 10 GB of available space
  4. Internet: Required for downloading datasets and optional cloud integration

Recommended Configuration

  1. Processor: Intel Core i7 or equivalent
  2. RAM: 16 GB or higher
  3. Storage: 20 GB or more, depending on dataset size
  4. GPU: Optional for small neural networks; beneficial for larger datasets and deep-learning models

8. Advantages of the Project

  1. Automates the identification of suspicious network activity.
  2. Uses neural networks to learn complex relationships between traffic features.
  3. Improves model efficiency through feature selection and parameter optimization.
  4. Supports binary and multi-class intrusion classification.
  5. Provides measurable performance comparisons between baseline and optimized models.
  6. Visualizes intrusion patterns and classification results.
  7. Can be extended to cloud-based security monitoring.
  8. Helps security teams prioritize suspicious events for investigation.


No review given yet!

Fast Delivery all across the country
Safe Payment
7 Days Return Policy
100% Authentic Products

You may also like

View all

Quantum Machine Learning-Based Intrusion Detection

₹4,999.00

Digital-Twin-Based Adaptive Intrusion Detection

₹4,999.00

Federated Intrusion Detection for Distributed Networks

₹4,999.00

IoT Botnet Attack Detection

₹4,999.00

Android Malware Classification using Deep Learning

₹4,999.00

Cloud Intrusion Detection using Optimized Neural Networks
₹4,999.00 ₹0.00
₹4,999.00
4999