1. Abstract
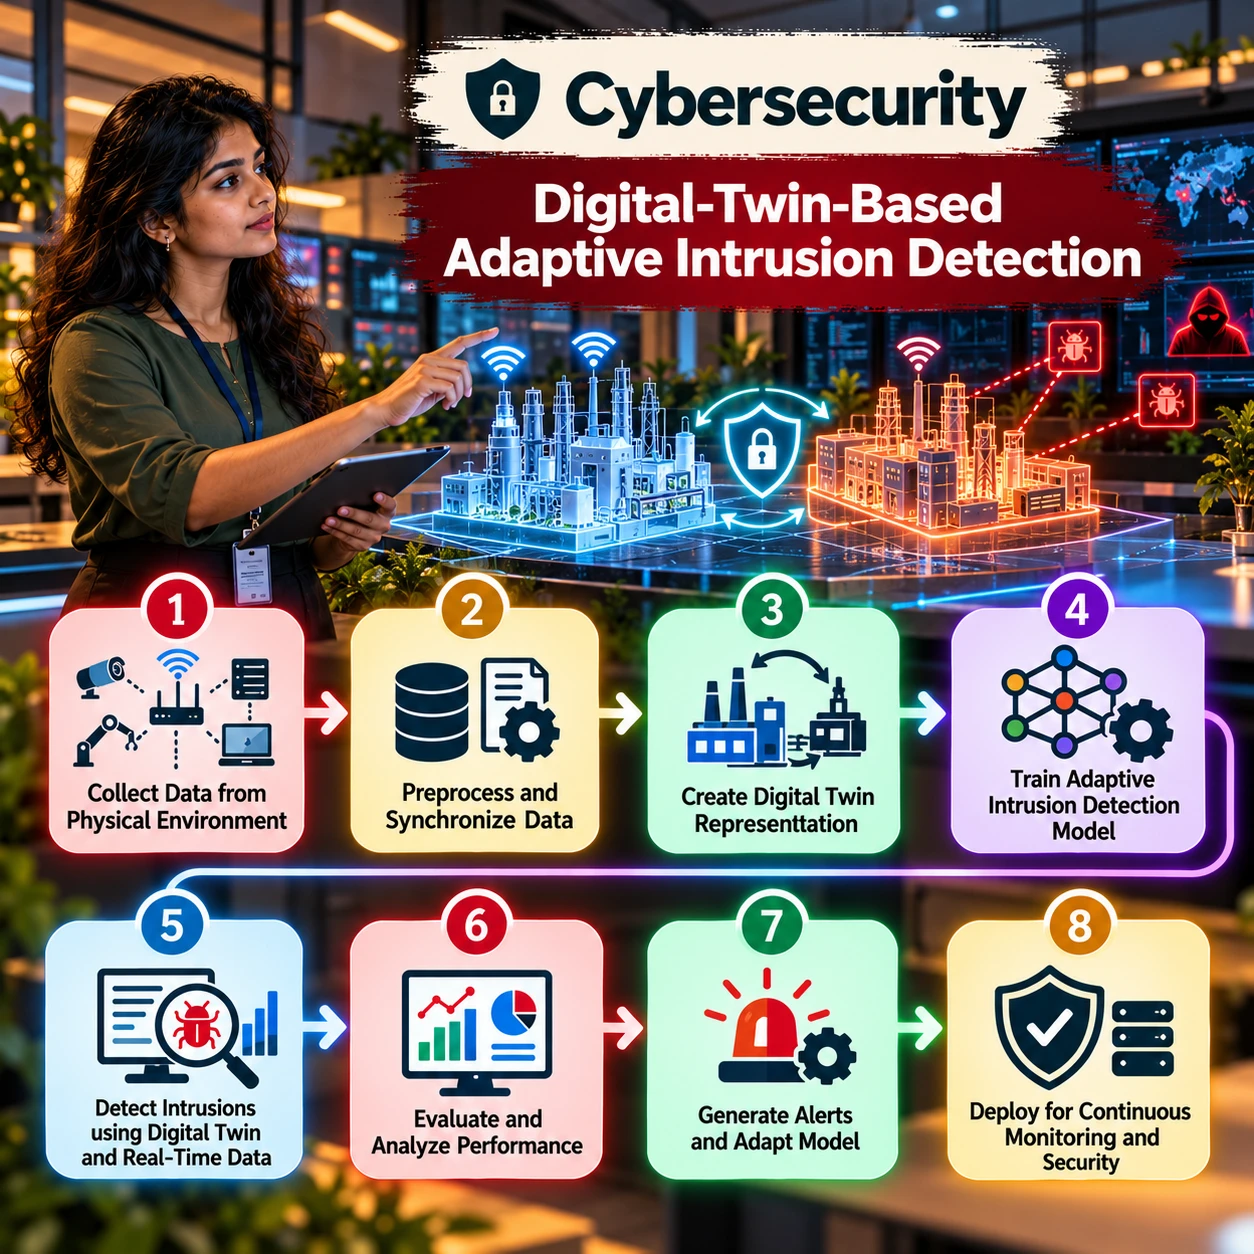
Digital-Twin-Based Adaptive Intrusion Detection is an intelligent cybersecurity project that combines digital twin technology with machine learning to monitor network behavior and detect potential security threats. A digital twin acts as a virtual representation of a physical or virtual network environment, allowing the system to simulate normal operations, observe traffic patterns, and identify deviations from expected behavior. The proposed system analyzes network traffic and operational data using machine-learning or deep-learning models to classify activities as benign or potentially malicious. An adaptive detection mechanism updates its detection thresholds or model parameters as network conditions change. A real-time monitoring dashboard displays the digital twin's status, detected anomalies, security alerts, and model performance. This approach supports continuous security monitoring and helps investigate suspicious behavior in dynamic network environments.
2. Objectives
- Develop a digital twin representation of a network or IoT environment.
- Monitor simulated or collected network traffic and operational metrics.
- Detect suspicious activities using machine-learning techniques.
- Adapt detection thresholds or models to changing network conditions.
- Compare observed behavior with the digital twin's expected behavior.
- Visualize anomalies, attack alerts, and system status.
- Evaluate detection accuracy, false-positive rates, and response latency.
- Support controlled simulation of normal and malicious network scenarios.
3. Existing System
Traditional intrusion detection systems rely on predefined rules, signatures, or machine-learning models trained on historical network data. Although these systems can identify known attack patterns, they may struggle when network behavior changes or when new attack patterns emerge. Conventional monitoring dashboards also tend to show observed traffic without maintaining a synchronized virtual representation of the monitored environment.
Disadvantages
- Static detection rules may not adapt to changing traffic patterns.
- Signature-based systems can miss previously unknown threats.
- Limited integration between network simulation and security monitoring.
- Changes in legitimate network behavior may generate false alerts.
- Retraining and updating detection models can require manual effort.
- Limited ability to test detection strategies against a virtual network before deployment.
4. Proposed System
The proposed system creates a digital twin of a network or IoT environment and connects it to a traffic-monitoring and intrusion-detection pipeline. The digital twin maintains a representation of network devices, connections, operational states, and expected behavior. A detection model analyzes observed traffic and identifies anomalies. An adaptive mechanism adjusts detection thresholds or updates the model based on validated changes in network behavior.
Key Features
- Digital Twin Simulation: Represents network devices, traffic flows, and operational states.
- Traffic Monitoring: Processes network-flow features and operational metrics.
- AI-Based Intrusion Detection: Classifies network activity as benign or potentially malicious.
- Adaptive Detection: Adjusts thresholds or model parameters as network conditions change.
- Anomaly Visualization: Highlights deviations between expected and observed behavior.
- Attack Scenario Simulation: Supports controlled testing of simulated attack patterns.
- Security Alerts: Displays suspicious events for further investigation.
- Interactive Dashboard: Shows network topology, traffic statistics, alerts, and detection performance.
- Model Evaluation: Measures precision, recall, F1-score, false-positive rate, and detection latency.
- Digital Twin Synchronization: Updates the virtual representation using incoming monitoring data.
5. Implementation Procedure
- Requirement Analysis: Select a target environment, such as an IoT network, enterprise network, or cloud infrastructure.
- Digital Twin Design: Create a virtual representation of devices, connections, traffic flows, and expected operational behavior.
- Dataset Collection: Obtain a suitable labeled network intrusion dataset, such as CICIDS2017 or an appropriate IoT traffic dataset.
- Data Preprocessing: Clean records, handle missing values, encode categorical features, and normalize numerical attributes where needed.
- Feature Engineering: Extract features such as flow duration, packet counts, byte rates, connection frequency, and protocol information.
- Baseline Detection Model: Train a suitable classifier, such as Random Forest, XGBoost, or an artificial neural network.
- Digital Twin Integration: Feed observed or simulated network data into the digital twin and compare it with expected behavior.
- Adaptive Mechanism Development: Implement controlled threshold adjustment, drift detection, or scheduled model retraining using validated data.
- Anomaly Detection: Identify unusual traffic patterns and correlate them with the virtual network's expected state.
- Dashboard Development: Build an interface to display network status, simulated events, detection results, and alerts.
- Performance Evaluation: Test normal and simulated attack scenarios, measuring detection accuracy, false positives, and processing latency.
- System Testing: Verify synchronization, adaptation behavior, and alert reliability before considering real-world deployment.
6. Software Requirements
- Programming Language: Python
- Machine Learning: Scikit-learn, XGBoost
- Deep Learning: TensorFlow/Keras or PyTorch
- Data Processing: Pandas, NumPy
- Visualization: Plotly, Matplotlib, or Seaborn
- Digital Twin Simulation: A Python-based simulation environment or a suitable digital twin platform
- Network Simulation: Mininet or an equivalent network simulation tool, if required
- Traffic Analysis: Zeek or Wireshark for authorized traffic monitoring, if required
- Backend: Flask or FastAPI
- Frontend: Streamlit or React.js
- Database: SQLite or PostgreSQL, if event and device persistence is needed
- Development Environment: VS Code, Jupyter Notebook, or Google Colab
- Operating System: Windows or Linux
7. Hardware Requirements
Minimum Configuration
- Processor: Intel Core i5 or equivalent
- RAM: 8 GB
- Storage: 10 GB of available space
- Network: Local network or internet connectivity for data collection and optional integration
Recommended Configuration
- Processor: Intel Core i7 or equivalent
- RAM: 16 GB or higher
- Storage: 20 GB or more, depending on datasets and simulation size
- GPU: Optional for traditional machine-learning models; useful for larger deep-learning models
- Additional Resources: Multiple virtual machines or containers for realistic distributed network simulation
8. Advantages of the Project
- Combines digital twin simulation with AI-based threat detection.
- Supports continuous monitoring of changing network behavior.
- Helps identify anomalies that may not match predefined attack signatures.
- Enables controlled testing of detection strategies in a virtual environment.
- Provides visual comparison between expected and observed network states.
- Supports adaptive detection when network conditions change.
- Helps analyze false positives and detection performance.
- Can be extended to IoT, cloud, industrial, and enterprise network environments.