-20%

Federated Intrusion Detection for Distributed Networks

0 Orders 0 Wish listed

₹4,999.00

Qty
Total price:
  ₹4,999.00

Detail Description

1. Abstract

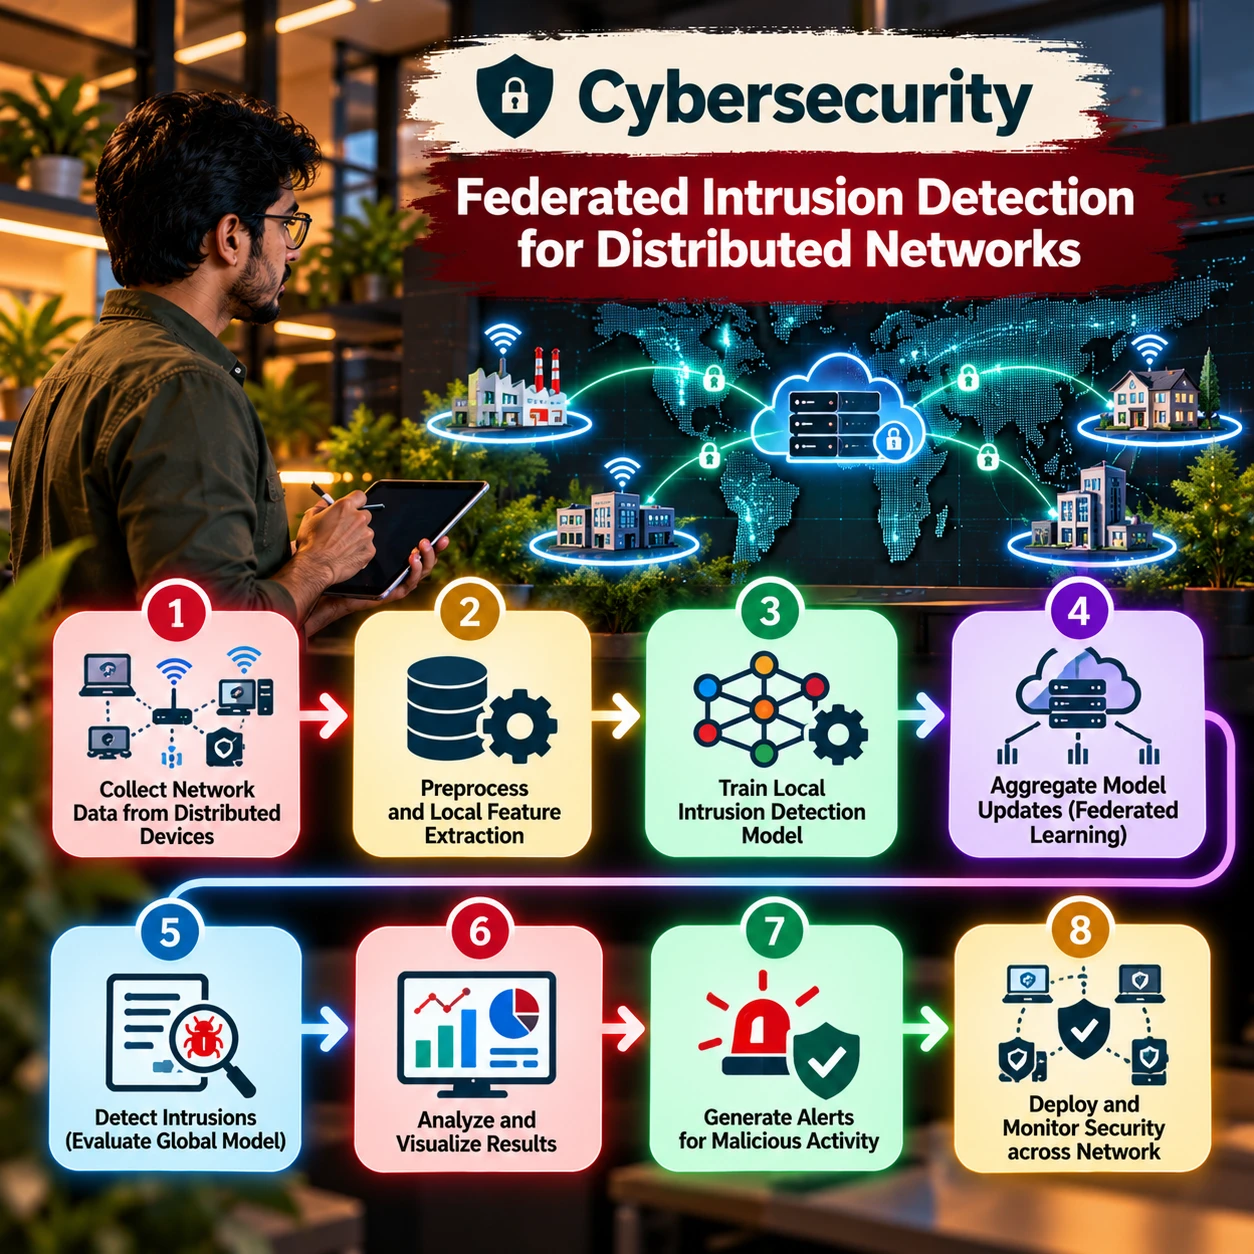
Federated Intrusion Detection for Distributed Networks is a cybersecurity project that uses Federated Learning (FL) to detect malicious network activities across multiple distributed environments without requiring all raw network traffic data to be centralized. Each participating network trains a local intrusion detection model using its own traffic data and shares model updates with a central aggregation server. The server combines these updates to create a global model that can benefit from patterns learned across participating networks. The system uses machine-learning or deep-learning algorithms to classify network traffic as benign or potentially malicious. A monitoring dashboard displays intrusion predictions, model performance, and network-level security insights. This approach aims to improve collaborative threat detection while reducing the need to exchange raw network data between participating organizations.

2. Objectives

  1. Develop a federated intrusion detection system for distributed networks.
  2. Train local models using data stored at individual network nodes.
  3. Aggregate model updates to build a shared global detection model.
  4. Reduce the need to transfer raw network traffic to a central server.
  5. Detect benign and malicious network activities.
  6. Evaluate the performance of federated learning against centralized and local-only training.
  7. Analyze model performance across heterogeneous network datasets.
  8. Visualize detection results and federated training progress through a dashboard.

3. Existing System

Traditional intrusion detection systems commonly collect network traffic or security logs in a centralized location for analysis. Centralized machine-learning models can learn from combined datasets, but transferring sensitive network data may introduce privacy, bandwidth, and governance concerns. Independent local models avoid central data collection but may lack the broader knowledge available from multiple participating networks.

Disadvantages

  1. Centralized training may require transferring sensitive network data.
  2. Data sharing can create privacy and regulatory concerns.
  3. Local-only models may have limited exposure to diverse attack patterns.
  4. Centralized data collection can increase storage and communication requirements.
  5. Different networks may have different traffic distributions and attack types.
  6. Conventional systems may not support collaborative model training across organizations.

4. Proposed System

The proposed system implements a Federated Learning framework in which multiple network clients train local intrusion detection models. Instead of transmitting raw traffic records, clients send model updates to a central aggregation server. The server combines these updates using an algorithm such as Federated Averaging (FedAvg) and distributes the updated global model back to participating clients.

Key Features

  1. Distributed Local Training: Each client trains a model on its own network traffic data.
  2. Federated Model Aggregation: Combines client updates into a global intrusion detection model.
  3. Intrusion Classification: Identifies benign and potentially malicious traffic.
  4. Multi-Class Detection: Supports multiple attack categories when suitable labeled datasets are available.
  5. Privacy-Aware Architecture: Keeps raw training data on participating clients by design.
  6. Heterogeneous Data Support: Evaluates performance when networks have different traffic patterns.
  7. Model Performance Monitoring: Displays accuracy, precision, recall, F1-score, and false-positive rates.
  8. Client Management: Shows participating clients and their training status.
  9. Dashboard Visualization: Presents global model performance, local results, and training progress.
  10. Secure Communication Extension: Can incorporate authenticated connections, encrypted transport, and secure aggregation.

Note: Federated Learning reduces the need to share raw data, but model updates can still leak information. Additional privacy and security measures may be necessary.

5. Implementation Procedure

  1. Requirement Analysis: Define the participating network clients, attack categories, privacy requirements, and model evaluation goals.
  2. Dataset Collection: Select an intrusion detection dataset, such as CICIDS2017, CSE-CIC-IDS2018, or another suitable labeled network traffic dataset.
  3. Distributed Data Preparation: Partition the dataset across multiple simulated clients to represent different network environments.
  4. Data Preprocessing: Handle missing values, encode categorical features, normalize numerical variables, and address class imbalance.
  5. Local Model Development: Build a neural network or machine-learning classifier for local intrusion detection.
  6. Federated Learning Setup: Configure client training and a central server using a framework such as Flower.
  7. Local Training: Train each client model using only that client's local dataset.
  8. Model Aggregation: Apply FedAvg or another suitable aggregation algorithm to combine model updates.
  9. Global Model Distribution: Send the updated global model back to participating clients for subsequent training rounds.
  10. Performance Evaluation: Compare federated, centralized, and local-only models using precision, recall, F1-score, and false-positive rates.
  11. Dashboard Development: Build a dashboard using Streamlit or React.js to display client status, training rounds, and detection results.
  12. Security Testing: Evaluate client failures, data heterogeneity, communication security, and potential poisoning or privacy attacks where appropriate.

6. Software Requirements

  1. Programming Language: Python
  2. Federated Learning Framework: Flower
  3. Machine Learning: Scikit-learn
  4. Deep Learning: TensorFlow/Keras or PyTorch
  5. Data Processing: Pandas, NumPy
  6. Visualization: Matplotlib, Seaborn, or Plotly
  7. Dataset: CICIDS2017, CSE-CIC-IDS2018, or another suitable intrusion detection dataset
  8. Backend: Flask or FastAPI, if required
  9. Frontend: Streamlit or React.js
  10. Communication Security: TLS-enabled communication for distributed deployments
  11. Development Environment: VS Code, Jupyter Notebook, or Google Colab
  12. Operating System: Windows or Linux

7. Hardware Requirements

Minimum Configuration

  1. Processor: Intel Core i5 or equivalent
  2. RAM: 8 GB
  3. Storage: 10 GB of available space
  4. Network: Internet or local network connectivity for client-server communication

Recommended Configuration

  1. Processor: Intel Core i7 or equivalent
  2. RAM: 16 GB or higher
  3. Storage: 20 GB or more, depending on dataset size and the number of clients
  4. GPU: Optional for small models; beneficial for larger deep-learning models
  5. Distributed Environment: Multiple virtual machines, containers, or computers for realistic client simulations

8. Advantages of the Project

  1. Reduces the need to centralize raw network traffic data.
  2. Enables collaborative learning across distributed networks.
  3. Combines knowledge from multiple clients into a shared model.
  4. Supports local and global intrusion detection evaluation.
  5. Can accommodate different network environments and attack categories.
  6. Provides a scalable architecture for distributed cybersecurity.
  7. Supports monitoring of federated training and model performance.
  8. Can be extended with secure aggregation and differential privacy.


No review given yet!

Fast Delivery all across the country
Safe Payment
7 Days Return Policy
100% Authentic Products

You may also like

View all

Quantum Machine Learning-Based Intrusion Detection

₹4,999.00

Digital-Twin-Based Adaptive Intrusion Detection

₹4,999.00

Cloud Intrusion Detection using Optimized Neural Networks

₹4,999.00

IoT Botnet Attack Detection

₹4,999.00

Android Malware Classification using Deep Learning

₹4,999.00

Federated Intrusion Detection for Distributed Networks
₹4,999.00 ₹0.00
₹4,999.00
4999