-20%

VANET Malicious Node Detection using XAI

0 Orders 0 Wish listed

₹4,999.00

Qty
Total price:
  ₹4,999.00

Detail Description

Heterogeneous Edge Data


1. VANET Malicious Node Detection Using XAI

1. Abstract

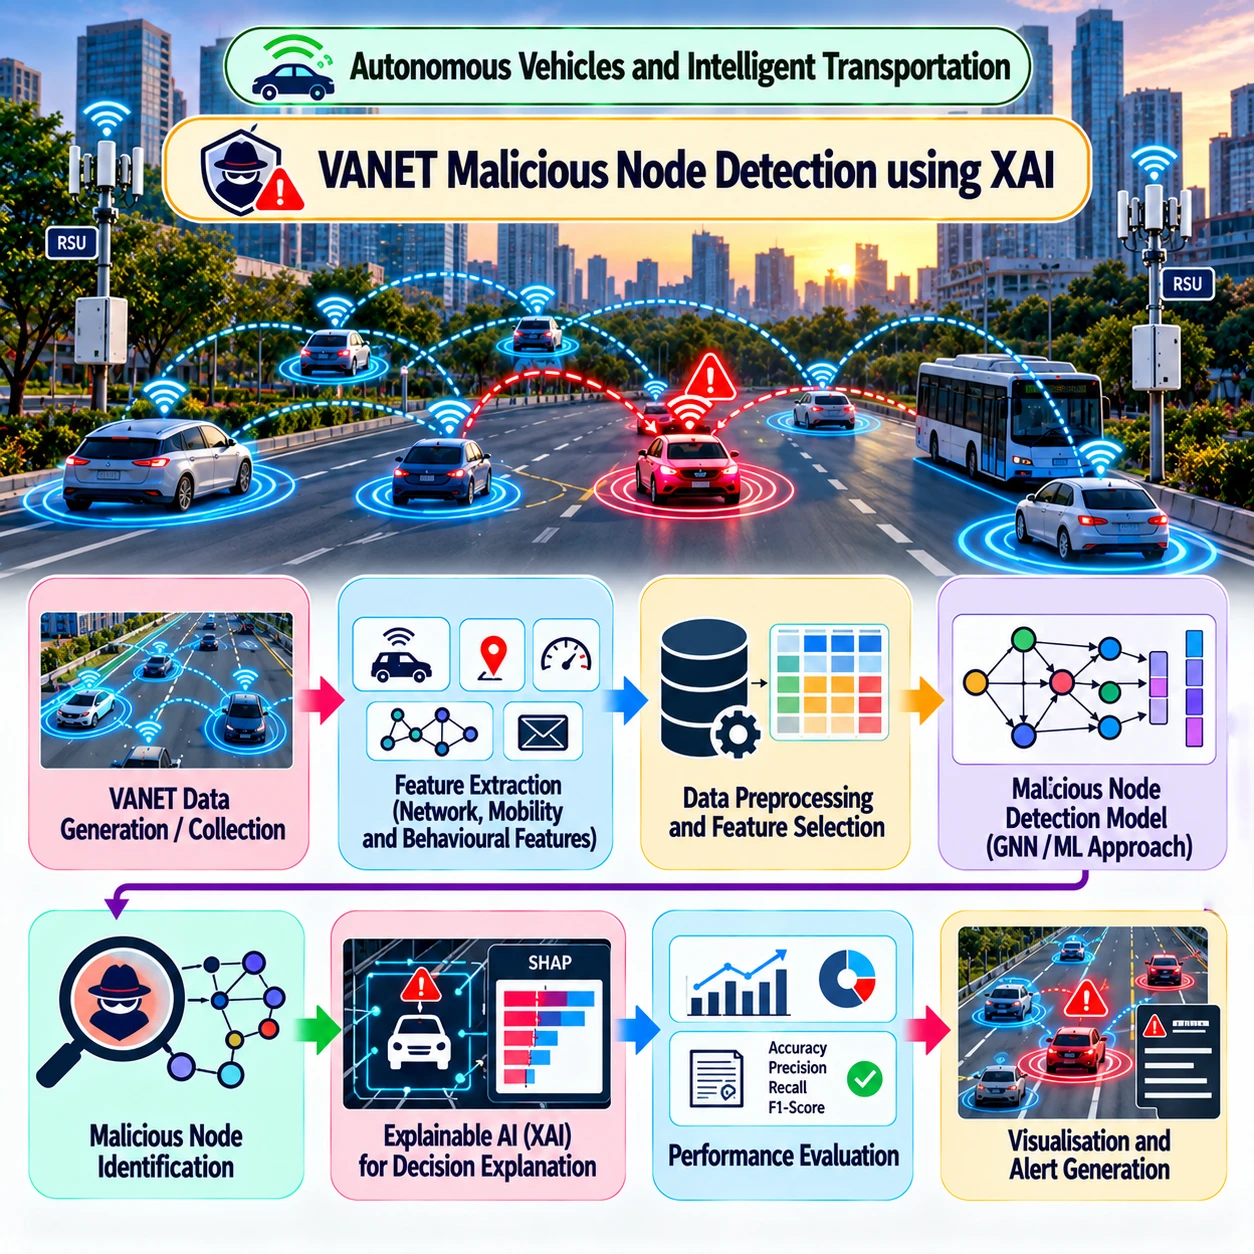
VANET Malicious Node Detection Using Explainable Artificial Intelligence (XAI) is a cybersecurity project designed to identify malicious vehicles and suspicious communication behavior in Vehicular Ad Hoc Networks (VANETs). VANETs enable vehicles to exchange safety and traffic information with nearby vehicles and roadside infrastructure. However, malicious nodes may transmit false messages, impersonate legitimate vehicles, or disrupt network communication. This project uses machine learning techniques to classify network nodes as normal or potentially malicious based on communication and behavioral features. Explainability techniques such as SHAP or LIME help interpret the model's predictions by identifying the features that contribute to suspicious classifications. The system provides a monitoring dashboard with detection results, risk indicators, and explanations to support transparent and trustworthy VANET security analysis.

2. Objectives

  1. To detect malicious nodes in vehicular ad hoc networks.
  2. To analyze vehicle communication and network behavior.
  3. To classify nodes as normal or potentially malicious.
  4. To apply machine learning for intrusion and anomaly detection.
  5. To explain model predictions using XAI techniques such as SHAP or LIME.
  6. To identify important features associated with suspicious behavior.
  7. To visualize detection results and explanations through a dashboard.

3. Existing System

Traditional VANET security systems use rule-based detection, cryptographic mechanisms, or machine learning models to identify suspicious network activity. Although these approaches can help protect vehicle communication, some detection models provide limited insight into why a node was classified as malicious.

Disadvantages:

  1. Rule-based systems may struggle with previously unseen attack patterns.
  2. Some machine learning models provide limited interpretability.
  3. False positives can incorrectly flag legitimate vehicles.
  4. Changing network conditions may affect detection performance.
  5. Security analysts may find it difficult to understand complex model predictions.

4. Proposed System

The proposed system combines machine learning-based malicious node detection with explainable AI. Network traffic and vehicle behavior data are preprocessed and analyzed to identify suspicious communication patterns. A trained classifier predicts whether a node is normal or potentially malicious. XAI techniques then explain individual predictions and highlight influential features, such as abnormal message frequency, unusual packet behavior, or inconsistent mobility information, when those features are available in the dataset.

Key Features:

  1. Malicious node classification.
  2. VANET communication behavior analysis.
  3. Machine learning-based threat detection.
  4. Explainable predictions using SHAP or LIME.
  5. Feature importance visualization.
  6. Suspicious node risk scoring.
  7. Detection history and monitoring dashboard.
  8. Model performance evaluation and false-positive analysis.

5. Implementation Procedure

  1. Data Collection: Obtain a suitable VANET dataset containing normal and malicious communication records, such as a relevant vehicular network intrusion detection dataset.
  2. Data Preprocessing: Clean missing values, remove duplicates, encode categorical features, and normalize numerical variables where required.
  3. Feature Engineering: Extract useful communication and behavior features, such as packet rates, packet delivery patterns, message intervals, network flow statistics, or mobility indicators, depending on dataset availability.
  4. Dataset Splitting: Divide the data into training, validation, and test sets while avoiding leakage between records from the same scenario or vehicle where appropriate.
  5. Model Development: Train classification models such as Random Forest, XGBoost, or a neural network to distinguish normal nodes from malicious nodes.
  6. Model Evaluation: Evaluate precision, recall, F1-score, confusion matrix, and false-positive rate to assess detection quality.
  7. XAI Integration: Apply SHAP or LIME to explain predictions and identify which features contributed most to each classification.
  8. Risk Classification: Assign risk levels to suspicious nodes based on model scores and validated thresholds.
  9. Dashboard Development: Create a dashboard showing node classifications, detection statistics, feature importance, and individual prediction explanations.
  10. Testing and Validation: Test the complete pipeline using unseen data and, if possible, simulated VANET scenarios containing different attack types.

6. Software Requirements

ComponentRecommended Technology
Programming LanguagePython
Data ProcessingPandas, NumPy
Machine LearningScikit-learn, XGBoost
Explainable AISHAP, LIME
Network Simulation (Optional)SUMO, OMNeT++, or Veins
Network Analysis (Optional)Wireshark
Data VisualizationMatplotlib, Plotly
DashboardStreamlit or Flask
DatabaseSQLite or PostgreSQL
Development EnvironmentVS Code or Jupyter Notebook

7. Hardware Requirements

ComponentRecommended Specification
ProcessorIntel Core i5 or equivalent
RAM8 GB minimum; 16 GB recommended
Storage256 GB SSD or higher
GPUOptional for traditional ML models; useful for deep learning
NetworkLocal network or internet for datasets and optional simulation
Operating SystemWindows or Linux
DisplayStandard monitor for the dashboard

8. Advantages of the Project

  1. Identifies potentially malicious nodes in VANET environments.
  2. Supports machine learning-based network security analysis.
  3. Explains why individual nodes are classified as suspicious.
  4. Helps analysts understand influential detection features.
  5. Supports evaluation of false positives and missed attacks.
  6. Provides visual monitoring of detection results.
  7. Can be extended to different vehicular network attack scenarios.
  8. Supports research into transparent and interpretable cybersecurity systems.

9. Search Tags

VANET Malicious Node Detection, Explainable AI, XAI for VANET Security, Vehicular Ad Hoc Networks, Malicious Vehicle Detection, VANET Intrusion Detection, Machine Learning Cybersecurity, SHAP Explainability, LIME Explainable AI, Vehicular Network Security, Anomaly Detection, False Data Injection Detection, Network Attack Classification, Intelligent Transportation Security, XGBoost Intrusion Detection

10. Meta Title

VANET Malicious Node Detection Using Explainable AI

11. Meta Description

Detect malicious nodes in VANETs using machine learning and explainable AI to identify suspicious vehicle communication and interpret security predictions.

Important note: XAI explains model behavior but does not guarantee that a prediction is correct. The system should be evaluated on representative attack scenarios and unseen data before any real-world security decisions are made.

2. Federated Multi-View Learning for Heterogeneous Edge Data

1. Abstract

Federated Multi-View Learning for Heterogeneous Edge Data is a distributed machine learning project designed to train collaborative AI models across edge devices containing different types of data. These data views may include sensor readings, images, time-series measurements, and operational records. Instead of transferring all raw data to a central server, each client processes its local data and contributes compatible model updates to the federated learning process. Multi-view representation learning combines information from different sources, while the federated framework supports collaborative model development. The project evaluates model performance, data heterogeneity, communication overhead, and convergence across distributed clients.

2. Objectives

  1. To develop a federated learning framework for multiple edge clients.
  2. To learn useful representations from multiple data views.
  3. To handle heterogeneous feature spaces and data distributions.
  4. To reduce the need to transfer raw data to a central server.
  5. To investigate model performance under non-IID client data.
  6. To measure communication costs and training convergence.
  7. To support privacy-conscious collaborative machine learning.

3. Existing System

Traditional centralized learning gathers data from multiple devices and transfers it to a central server for training. Standard federated learning distributes training across clients but often assumes compatible model architectures and feature spaces. These assumptions can be difficult to satisfy when devices collect different types of data or have different available features.

Disadvantages:

  1. Centralized data collection can create privacy and communication concerns.
  2. Heterogeneous data may reduce model performance.
  3. Different feature spaces can complicate model aggregation.
  4. Non-IID data may slow or destabilize convergence.
  5. Repeated communication can increase network overhead.

4. Proposed System

The proposed system combines multi-view representation learning with federated training. Each client processes its locally available data views through suitable encoders, producing representations or model updates that can be combined through a compatible aggregation strategy. A central coordinator manages training rounds without requiring all raw datasets to be uploaded. The system evaluates the impact of data heterogeneity, missing views, and different aggregation strategies on predictive performance.

Key Features:

  1. Distributed training across multiple edge clients.
  2. Multi-view feature extraction and representation fusion.
  3. Support for heterogeneous local datasets.
  4. Federated model aggregation.
  5. Reduced need for raw-data transfer.
  6. Evaluation under non-IID data distributions.
  7. Training metrics and client participation dashboard.
  8. Configurable communication rounds and client sampling.

5. Implementation Procedure

  1. Data Collection: Select a dataset with multiple data views or prepare separate datasets representing different edge data sources.
  2. Client Simulation: Divide the dataset among multiple clients with different data distributions and available feature sets.
  3. Data Preprocessing: Clean missing values, normalize numerical features, encode categorical values, and prepare each view for model training.
  4. Representation Learning: Create suitable encoders for each data view and combine representations using concatenation, attention, or a shared latent space.
  5. Local Training: Train models on individual clients while keeping their raw datasets local.
  6. Federated Aggregation: Aggregate compatible model parameters using methods such as Federated Averaging (FedAvg), where model structures permit.
  7. Heterogeneity Handling: Evaluate strategies for missing views, different feature spaces, and non-IID data distributions.
  8. Model Evaluation: Measure accuracy, precision, recall, F1-score, convergence, and communication overhead.
  9. Dashboard Development: Display training rounds, participating clients, global model performance, and communication statistics.
  10. Testing: Compare the federated approach with appropriate centralized and single-view baselines.

6. Software Requirements

ComponentRecommended Technology
Programming LanguagePython
Deep LearningPyTorch or TensorFlow
Federated LearningFlower or custom federated simulation
Data ProcessingPandas, NumPy
Machine LearningScikit-learn
Multi-View LearningCustom neural network encoders
VisualizationMatplotlib, Plotly
DashboardStreamlit or Flask
DatabaseSQLite or PostgreSQL
Development EnvironmentVS Code or Jupyter Notebook

7. Hardware Requirements

ComponentRecommended Specification
ProcessorIntel Core i5 or equivalent
RAM8 GB minimum; 16 GB recommended
Storage256 GB SSD or higher
GPUOptional; recommended for larger deep learning models
Edge ClientsMultiple computers, virtual clients, or edge devices
NetworkLocal network or internet for federated communication
Operating SystemWindows, Linux, or macOS

Note: Multiple virtual clients can be simulated on one computer for a student prototype. Physical edge devices are optional unless real-world deployment is required.

8. Advantages of the Project

  1. Enables collaborative learning across distributed devices.
  2. Reduces the need to centralize raw datasets.
  3. Supports learning from multiple data views.
  4. Provides a framework for handling heterogeneous client data.
  5. Enables evaluation of non-IID data and aggregation strategies.
  6. Supports communication-efficient model training experiments.
  7. Can be adapted to IoT, healthcare, industrial monitoring, and smart-city applications.
  8. Encourages privacy-conscious data processing, although federated learning alone does not guarantee privacy.


No review given yet!

Fast Delivery all across the country
Safe Payment
7 Days Return Policy
100% Authentic Products

You may also like

View all

Explainable Decision-Making for Autonomous Vehicles

₹4,999.00

Sensor-Fusion-Based Autonomous Navigation

₹4,999.00

Cooperative Perception for Connected Vehicles

₹4,999.00

Digital Twin for Autonomous Vehicle Networks

₹4,998.99

Reinforcement Learning-Based Traffic Signal Control

₹4,999.00

VANET Malicious Node Detection using XAI
₹4,999.00 ₹0.00
₹4,999.00
4999